


In the early stages of the generative AI wave, most attention focused on the ability to converse and create content. Users asked questions, the model processed the request, and then provided an answer within the same interaction session. This use remains useful, but it has clear limitations: AI often stops at suggesting information, while users must verify, decide, and carry out the next steps themselves.
Agentic AI aims for a different operating model. Instead of merely responding to a single request, the system can analyze a goal, break the work into multiple steps, use authorized tools, observe the results, and then adjust its actions. In other words, AI is moved from the role of a respondent to that of an agent helping carry out tasks.
This does not mean that every chatbot has already become a “virtual employee” capable of freely doing everything. Agentic AI is an architecture made up of multiple components, with the language model serving only as the reasoning center. The system’s effectiveness and safety also depend on data, tools, access restrictions, approval processes, and activity-logging mechanisms.
How is agentic AI different from an ordinary chatbot?
An ordinary chatbot typically handles a single conversational exchange in a question-and-answer format. If a user asks it to plan a business trip, the chatbot may suggest an itinerary, list options, or draft an email. However, the user still has to open the relevant applications, check the schedule, find information, and send the email themselves.
An agentic AI system can be designed to carry out that chain of work in a unified workflow. It can receive a high-level goal, identify missing information, query permitted data sources, compare options, create a draft, and pause to wait for human approval before taking an action with real-world consequences.
The important difference lies in the ability to maintain state and respond according to the outcome of each step. If a tool returns an error, the agent can try another approach or report that the task cannot yet be completed. If new data conflicts with the original plan, the system can update the plan rather than simply repeating its previous answer.
However, the concept of “autonomy” needs to be understood cautiously. AI has neither human will nor legal responsibility. Its degree of autonomy is only the range of actions designed in advance by people and organizations. A system that is allowed to read internal documents but not send emails is entirely different from one that can create orders or change customer data.
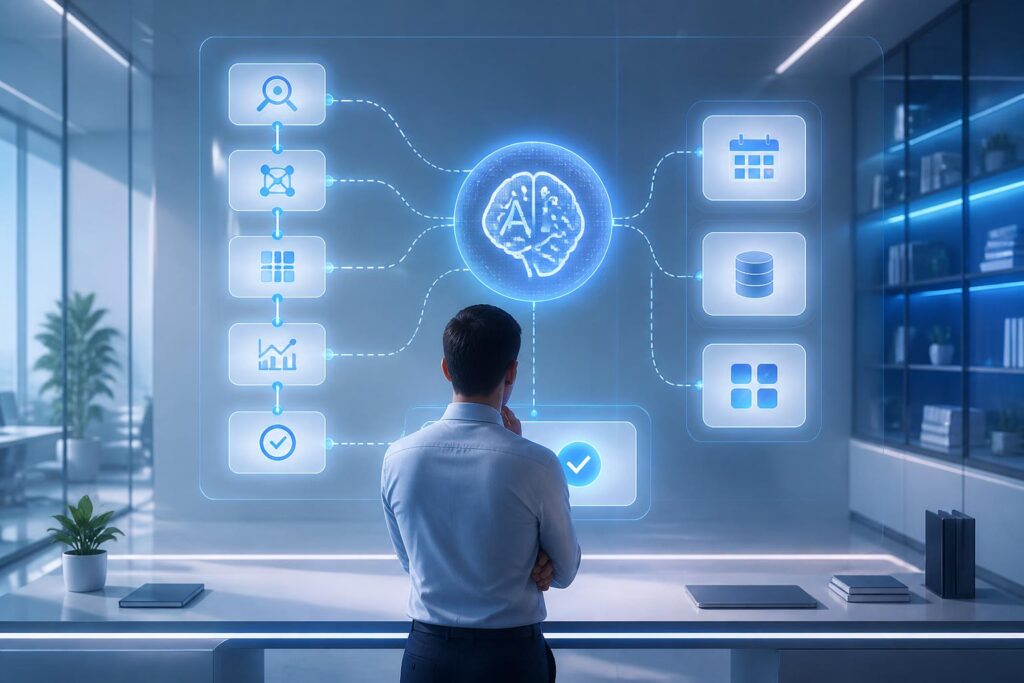
The basic structure of an agentic AI system
An agentic system usually starts with a goal provided by a user or business. The clearer the goal, the better the ability to control it. “Find a suitable option” is a very broad request, whereas “compare three options according to budget, deadline, and return conditions” creates criteria that are easier to verify.
After receiving the goal, the model can create a plan. This plan does not necessarily have to be perfect from the outset. The system can divide the task into smaller steps, identify the tools needed, and predict the expected result of each step. For complex tasks, planning helps reduce rambling responses or the omission of important conditions.
The next component is the toolset. Tools may include search functions in a document repository, a calendar management system, data analysis software, an internal database, or an application programming interface. AI does not automatically have access to these systems. Each permission must be configured specifically—for example, read-only access, permission only to create drafts, or permission to perform actions within a certain scope.
Memory is also a noteworthy component. The agent needs to know what has happened in the current work session, which steps have been completed, and which results need to be retained. Some systems also store information long term to personalize assistance, but this storage must comply with data policies. Not every piece of information a user has provided should be kept indefinitely.
Finally, there is the monitoring and evaluation layer. The system needs to record the request, the plan, the tools used, the results returned, and the final action. This log helps people trace errors when something goes wrong and provides a basis for improving the process. If an organization looks only at the final answer, it may not know whether the error originated in the data, the tool, or a particular reasoning step.
Potential applications
In businesses, agentic AI can support repetitive processes that still require the handling of language and inconsistent information. For example, an agent can receive a customer support request, find the relevant policy, check the order status, draft a response, and transfer the case to an employee when it encounters an exception. The value lies not in replacing all employees but in shortening preparatory steps and reducing manual work.
In internal departments, an agent can help compile documents, cross-check procedures, prepare reports, or track tasks. Employees still need to review important content, but they do not have to start from a blank page. For technical teams, the system can help analyze errors, suggest testing methods, and create draft documentation. These activities are better suited to a model with approval because they produce intermediate outputs for people to review.
In education, agentic AI can serve as a teaching assistant aligned with specific learning objectives. It can ask guiding questions, identify areas of weakness in a learner’s knowledge, and adjust practice exercises. However, such a system should not be given full authority to assess ability if its criteria are not transparent. Learning outcomes directly affect students, so teachers need the ability to review and explain decisions.
At the individual level, an agent can help manage schedules, organize work, or prepare trips. These are appealing areas because users can easily see the benefit of reducing the number of steps. Even so, tasks involving purchases, finances, private information, or communication with other people should include a clear confirmation step before the system acts.
Risks increase when AI is given authority
An incorrect chatbot response is already a matter of concern, but an agent taking the wrong action can have more serious consequences. Inaccurate information in a draft can be corrected before it is sent. In contrast, if the system automatically sends the wrong notification, incorrectly updates data, or books an unsuitable service, correcting the problem can take considerable time and money.
The first risk is an ambiguous goal. When a request does not clearly state priorities, AI may optimize in a way that does not match actual intentions. For example, a system asked to reduce costs might choose a cheaper option that increases the time required or lowers quality. Therefore, goals need to be accompanied by conditions, limits, and evaluation criteria.
The second risk is malicious data or hidden instructions in documents. An agent that reads multiple sources may encounter content designed to deceive it, causing the system to disclose information or use tools for the wrong purpose. Allowing the model to treat every piece of text it finds as an instruction is dangerous design. Reference data must be distinguished from instructions that have the authority to control the system.
The third risk concerns access permissions. Granting too many permissions so that the system can “work conveniently” expands the scope of damage when an error occurs. The appropriate principle is to grant only the minimum permissions necessary, separate read and write access, and limit actions according to each type of task. Actions that cannot be reversed should require human confirmation.
In addition, organizations need to address privacy and accountability. When an agent processes emails, customer records, or internal documents, users must know what data is being used, where it is stored, and who can access it. When an incident occurs, it should also be clearly established who is responsible for checking, who approves, and who has the authority to stop the system.
How to deploy it cautiously
Businesses should not begin by handing an important process over to AI and expecting the system to perfect it on its own. A safer approach is to choose a narrowly scoped task that occurs frequently enough to create value and whose consequences in the event of error can be controlled. In the initial phase, priority should be given to tasks that create drafts, classify, or make recommendations rather than act directly.
Each process needs specific success criteria. Organizations can evaluate the accuracy of results, time saved, the rate at which cases must be transferred to people, and the number of times the system uses the wrong tool. These criteria help organizations see both benefits and costs instead of relying only on the feeling that the system is becoming “smarter.”
Designing the approval interface is no less important than designing the model. Reviewers need to see the data sources, the reasons for the recommendation, the changes the action will create, and how to undo it when possible. An approval button without the necessary information creates only a sense of control; it does not necessarily help people exercise real control.
Finally, the system must be tested in unusual situations. Questions need to be asked about missing data, unavailable tools, conflicting requests, denied access permissions, and users intentionally providing dangerous instructions. Testing does not end when the product is put into use, because an organization’s data, processes, and goals can change over time.
Real value lies in process design
Agentic AI opens up the possibility of automating many tasks that previously required people to coordinate across multiple software applications. But this capability should not be evaluated solely by how natural the model’s answers sound. The more important questions are whether the system correctly understands the goal, uses the right data, acts within the proper limits, and can explain the process when something goes wrong.
In practice, a trustworthy agent may not be the system that does the most work on its own. It may be the system that knows when to ask for clarification, when to stop, when to hand a task over to a person, and when there is not enough information to reach a conclusion. This caution helps AI become a manageable layer of support rather than a black box given excessive authority.
Therefore, adopting agentic AI should be viewed as a process-design and risk-management problem, not merely as a choice of language model. When authority is clearly divided, data is protected, actions are recorded, and people retain decision-making power at important points, agentic AI can create sustainable productivity without turning convenience into a new source of risk.
