

In the early stages of the generative AI wave, most users interacted with the technology through a chat window. They asked questions, requested summaries, drafted content, or sought ideas, then checked the results themselves and carried out the next steps. This model remains useful, but a new direction is attracting attention: agentic AI, or AI systems capable of pursuing a goal through multiple steps and interacting with external tools.
The important difference is that agentic AI does not merely generate an answer. Depending on how it is designed, the system can analyze a request, make a plan, retrieve data, call software, evaluate intermediate results, and then continue taking action. This opens up the possibility of automating many repetitive processes, while also raising larger questions about access rights, accountability, and how people control machines.
Agentic AI is not a term meant to turn every piece of software into a “virtual employee” that can make unlimited decisions on its own. A more practical understanding is that it is a system consisting of an AI model, instructions, data, authorized tools, and control rules. The quality of the system depends on this entire structure, not just on the model’s language capabilities.
How Is Agentic AI Different from a Conventional Chatbot?
A conventional chatbot usually responds directly based on the content provided by the user and the data it is allowed to access. If they want to carry out a longer task, users generally have to divide it into multiple requests and connect the results themselves. Agentic AI can take over part of this connecting work by turning a broad goal into a series of specific steps.
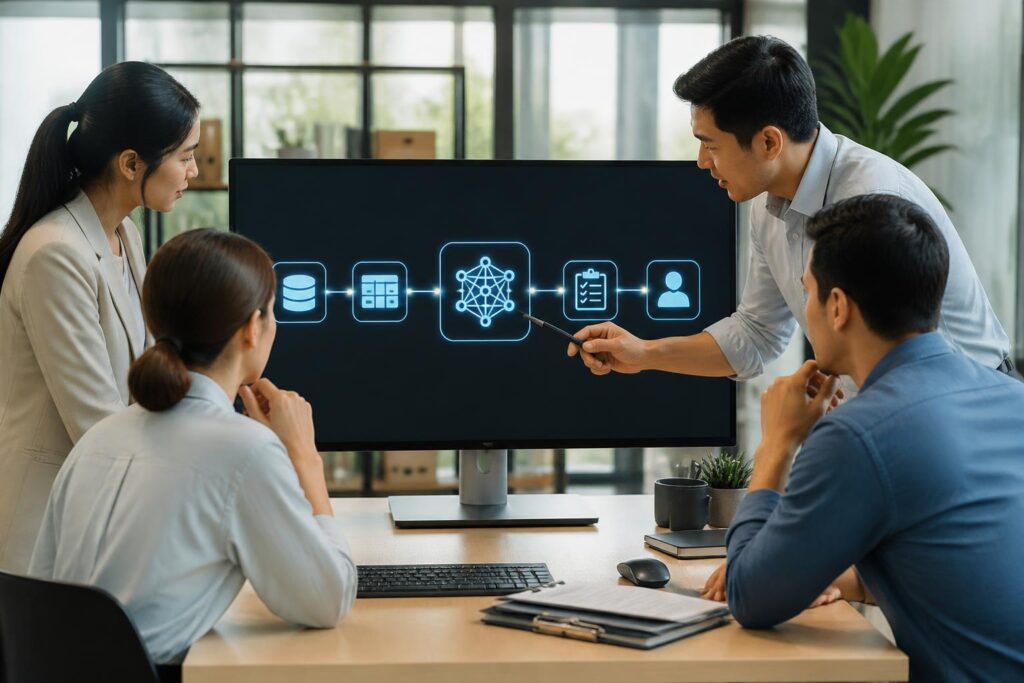
For example, for a request to prepare an internal report, a system could be designed to retrieve data from designated sources, filter the necessary fields, identify missing information, create a draft, and send it to the person responsible for review. Each step requires clear rules. The system should not access all data or send documents externally simply because the initial instruction appears reasonable.
Another difference is the ability to use tools. These tools may include document repositories, task management software, customer service systems, or data analysis applications. Agentic AI does not “know” these systems in the way people use them; it must be connected through specific interfaces and permissions. If a connection is configured incorrectly, a task that appears simple can produce unintended consequences.
Practical Value Lies in the Process, Not the Name
Businesses are often drawn to demonstrations showing that AI can complete many tasks from a single assignment. However, sustainable value usually comes from processes with relatively clear inputs, verifiable outputs, and enough repetition for automation to provide benefits.
Processes suitable for experimentation often have several characteristics. First, the process objective is described specifically, such as categorizing support requests by group or preparing a summary from a defined set of documents. Second, the input data has a clear origin and does not change in ways that are too difficult to predict. Third, an employee can review the result before it creates a final impact. Finally, when the system makes a mistake, the business can detect and recover from it without causing serious harm.
By contrast, tasks directly related to legal, financial, personnel, or customer-benefit decisions require a cautious approach. AI can help collect and organize information, but giving an automated process full decision-making authority is a different matter. The more irreversible the consequences, the higher the need for human oversight.
Four Components to Design from the Start
Objectives and Scope
A well-functioning system needs to know what it is allowed to do and what it is not allowed to do. A description such as “handle every customer request” is too broad to serve as the basis for building safety mechanisms. A more specific description might limit the system to receiving questions, finding answers from an approved document repository, suggesting a response, and forwarding out-of-scope cases to an employee.
Limiting the scope does not make AI less useful. On the contrary, it helps businesses measure results and identify causes when errors occur. A small but stable task is often more valuable than a system advertised as capable of handling everything but difficult to verify.
Data and Reference Sources
Agentic AI should have access to only the data necessary for the task. This principle helps reduce the risk of information leaks and limits the possibility that the system will use outdated, unapproved, or irrelevant documents by mistake. Businesses should determine which data is the primary source, which data is for reference only, who is responsible for updates, and when the system must stop and ask the person in charge.
It is also necessary to distinguish between read and write permissions. A system may be allowed to read information in order to create a draft without necessarily being allowed to modify the original data. Separating these two types of permission is a simple way to reduce the impact when a process encounters a problem.
Tools and Permissions
Each connected tool should have a clear purpose. If AI only needs to create suggestions, consider not granting it permission to send emails, change order statuses, or delete data. Actions that can create external impacts should be placed behind a human confirmation step, especially when they involve customers, money, contractual commitments, or sensitive information.
Permissions should also be divided by role and time. A task that processes internal documents does not need to retain access indefinitely. When the process ends, temporary permissions should be revoked or automatically expire if the system supports such a mechanism.
Monitoring and Logs
A system cannot be managed without knowing what it has done. Logs should record the initial request, the data or tools used, the main steps, intermediate results, and the final action. This information helps employees investigate incidents, compare performance across versions, and identify areas for improvement.
Monitoring is not only about reviewing errors after they occur. Businesses can set stopping conditions, such as when data is missing, results conflict, costs exceed a threshold, or the system encounters a type of request outside its scope. A system that knows when to stop is often more reliable than one that always tries to complete every task.
Risks That Are Easily Overlooked
The first risk is that the system misunderstands the objective. A short request may conceal many conditions that the user assumes everyone knows. When AI divides a task on its own, it may choose a path that is linguistically reasonable but unsuitable for the actual process.
The second risk is unreliable data. If a reference source contains outdated or contradictory information, AI may create a consistent chain of actions based on a flawed foundation. Automation does not turn poor-quality data into correct data; it can only make the process of using that data happen faster.
The third risk comes from unintended expansion. A task given permission to read documents may inadvertently include sensitive content in a draft, log, or notification. A system with permission to take action may continue a chain of tasks even after the context has changed. Therefore, safe design needs to consider unusual paths as well as the ideal scenario.
Finally, there is the risk of dependence on a process that no one fully understands. When employees become accustomed to clicking a button and accepting the result, their ability to check the output may decline. Agentic AI should support human expertise, not cause an organization to lose the ability to explain how a decision or action was formed.
How to Start with a Small Project
The first step is to choose a process with a clearly designated owner. The person responsible does not necessarily have to be an engineer, but they need to understand the objective, data, quality criteria, and consequences of errors. Rather than starting with the question “What can AI do?”, begin with the question “Which steps in the process are time-consuming, repetitive, and verifiable?”
Next, document the current process before automating it. The description should specify the inputs, processing steps, approval points, exceptional cases, and desired outputs. This often exposes inconsistencies in the process that technology cannot resolve on its own.
During the pilot phase, use cleaned or non-sensitive data, limit the number of users, and retain a manual approval step. Businesses can track criteria such as time saved, the rate of required corrections, the number of times the system stopped at the right moment, and how easy it is to trace a result. These criteria are more practical than simply assessing whether the response sounds natural.
Before expanding, establish an incident-handling process. Employees must know how to stop a task, report an error, revoke access, and notify the responsible person. Without a recovery plan, even a system that performs well under normal conditions can become a burden when it encounters an unusual situation.
The Role of People Will Change
As AI takes on more repetitive steps, people can spend more time defining objectives, handling exceptions, and evaluating results. This does not mean that every employee must become a technical expert. However, they need to understand what the system is allowed to do, where its limits lie, and when a manual check is required.
Implementation teams also need coordination among business expertise, technology, security, and governance. A system built solely from a technical perspective may overlook practical needs; conversely, a process designed only around business preferences may grant overly broad permissions. Decisions about agentic AI therefore should not be treated as the responsibility of a single department.
Agentic AI can become a useful intermediary layer between people and the software they use every day. But to achieve that, businesses need to view it as a controlled process, not a magic solution capable of resolving every problem on its own. Starting with a narrow objective, clear data, minimal permissions, and an approval mechanism is a more reliable way to build a foundation.
Ultimately, the value of the technology does not lie in how many actions AI can perform, but in whether those actions serve the right purpose, can be explained, and remain under the organization’s control.
