


In the early stages of the artificial intelligence adoption wave, many organizations focused on tools capable of generating text, summarizing documents, or answering questions. Those tools remain useful, but the ways people use AI are gradually expanding. Instead of simply asking a system to produce an answer, users can assign AI a multi-step objective and expect the system to analyze the situation, choose actions, use relevant tools, and then report the results. This is the context in which the concept of agentic AI, or AI agents, has emerged.
Agentic AI is not a designation for every piece of software that incorporates AI. The key difference lies in its ability to pursue a goal through multiple steps, rather than simply responding to a single request. An agent can receive a task, break it down into smaller parts, check the necessary information, take actions within the permissions granted to it, and adjust its approach when the result does not meet requirements. However, this capability does not mean that AI can operate safely on its own in every situation. The technology’s practical value depends heavily on process design, data quality, and the level of human oversight.
How Does Agentic AI Work?
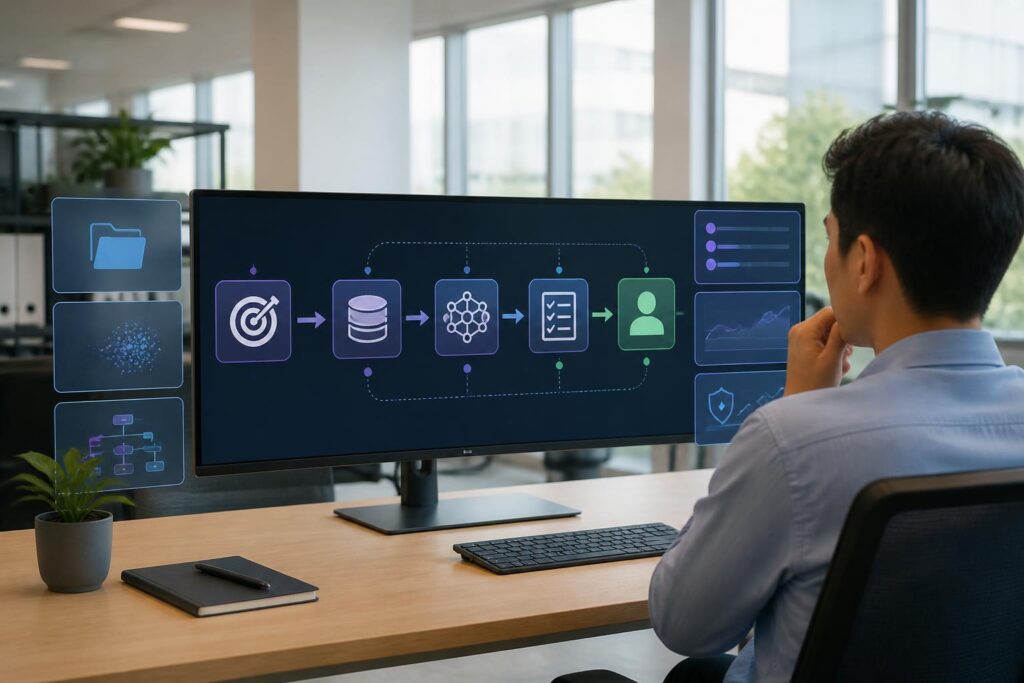
An agentic AI system typically consists of multiple components working together. First is the objective defined by the user or organization. The clearer the objective, the easier it is for the system to identify the desired outcome and the boundaries it must not cross. Next is an AI model capable of interpreting the request, reasoning about the processing steps, and selecting an appropriate approach. The system may also be connected to tools such as document repositories, work management software, databases, or internal services.
The process may begin with a relatively simple request, such as preparing a summary of customer feedback over a given period. To complete it, the agent may need to retrieve data from multiple sources, categorize opinions, identify recurring issues, create a draft report, and send the report to an employee for review. Each step can produce an intermediate result for the next step to use. If the system is well designed, users do not need to perform every manual operation themselves. Nevertheless, checkpoints still need to be placed at steps that significantly affect customers, finances, or management decisions.
The ability to remember the status of a task is also often mentioned when discussing agentic AI. A conventional chatbot may answer individual questions in a conversation, whereas an agent needs to track which step a task is currently at, what data has been collected, and which conditions are still missing. This requires a clear operating structure. Without mechanisms for recording status and handling errors, the system can easily repeat actions, skip important steps, or continue using an incorrect result.
The Difference Between an AI Assistant and an AI Agent
The boundary between an AI assistant and an AI agent is not always absolute, because many products can combine both approaches. An AI assistant can generally be understood as primarily supporting users with a specific task. The user asks a question, requests a draft, or asks for an analysis, then reviews it and decides what to do next. An AI agent has a higher degree of initiative: the system can identify the necessary sequence of actions and carry them out according to established rules.
This difference creates benefits but also raises governance requirements. When AI only provides a piece of text for the user to review, the scope of the risk is usually easier to contain. When AI can send emails, update records, create purchase requests, or change data in another system, a small error can lead to broader consequences. Therefore, agents should not be evaluated solely on how intelligently they respond. The ability to control, trace, stop, and limit access is equally important.
Areas That Could Benefit
In customer service, agentic AI can help classify requests, find information in a knowledge base, and prepare initial responses. Employees can still handle complex or sensitive cases, or those requiring specialized judgment. The reasonable goal here is not to replace the entire team, but to reduce the time spent on repetitive tasks and help route requests to the right department.
In internal operations, agents can help track project progress, remind people about upcoming tasks, summarize meeting minutes, or prepare lists of next steps. For human resources departments, systems can help search internal policies, direct employees to the correct forms, and compile frequently asked questions. In research and analysis, agents can organize documents, compare data sources provided by the organization, and create drafts for experts to evaluate.
These examples are meaningful only when the input data is sufficiently clear and the system’s permissions are appropriately designed. An agent cannot fully compensate for an inconsistent process. If each department uses a different term for the same type of record, or if data is stored without structure, the system can quickly produce results that are difficult to verify. Therefore, process standardization often needs to come before, or take place in parallel with, AI deployment.
Risks That Need to Be Considered from the Start
The first risk is that AI may misunderstand the objective or reach an inaccurate conclusion. When an incorrect answer exists only in a draft, an employee still has an opportunity to correct it. But if an agent automatically uses that result to carry out multiple subsequent steps, the initial error can spread. An effective system needs mechanisms for checking conditions, validating important data, and stopping when it encounters a situation outside the expected scope.
The second risk concerns access permissions. To complete a task, an agent may need to read or write data in multiple systems. If it is granted overly broad permissions, an unclear request could cause AI to access unnecessary information or take actions beyond the original objective. The appropriate principle is to grant only the minimum permissions needed for each task, separate read access from permission to change data, and record operations so they can be reviewed later.
The third risk is a lack of transparency. Users may know the final result but not understand which documents the system relied on, which steps it skipped, or why it chose a particular action. This makes it difficult to correct errors and assign responsibility. Businesses should require agents to provide processing logs at an easily readable level, identify the data sources used where permitted, and notify users when the system has had to make an inference or lacks sufficient information.
In addition, automating too quickly can weaken employees’ checking skills. When people become accustomed to accepting system-generated results, unusual signs may be overlooked. User training should therefore not focus only on how to write prompts for AI. Employees need to understand the technology’s limitations, know when to ask a person to review something, and know how to report a suspicious result.
How to Prepare for Deployment
Businesses do not necessarily need to begin with a system that has broad automation permissions. A more cautious approach is to select a process with a limited scope, relatively stable data, and verifiable results. Tasks such as summarizing internal information, classifying requests, or preparing drafts are generally more suitable for experimentation than decisions directly affecting the rights or benefits of customers and employees.
Before deployment, the objective, inputs, outputs, responsible person, and actions the AI is not allowed to perform should be clearly described. The process should also specify which situations require manual approval. For example, an agent may draft a reply but not send it; it may propose changes to a record but not update it automatically; or it may create a list of transactions requiring review without independently concluding that a transaction constitutes a violation.
The pilot phase needs to be evaluated using specific criteria. Businesses can consider accuracy, time saved, the number of times the system has to hand a task over to a person, common types of errors, and the ease of tracing actions. They should not rely solely on the impression that the tool responds quickly or produces fluent text. A trustworthy agent must produce results that fit the process and allow people to intervene when necessary.
Finally, responsibility should not be assigned entirely to the tool. AI can support processing and provide suggestions, but the organization still needs to determine who is responsible for the final decision, who monitors the system’s operation, and who has the authority to pause it. Internal policies also need to be updated when the agent is connected to new data or software.
From Technology Experimentation to Changing the Way We Work
Agentic AI has the potential to change how people divide up work. Instead of spending substantial time transferring data, searching for information, and performing repetitive steps, employees can focus more on judgment, communication, creativity, and handling exceptions. However, this change will not happen simply by purchasing a tool. It requires coordination among technology, processes, data, and a culture of accountability.
Viewing an AI agent as a fully autonomous employee can lead to misguided expectations. A more practical approach is to see it as an automation layer capable of handling multiple steps, but still required to operate within boundaries designed by people. When objectives are clear, permissions are sufficient but limited, data is well managed, and control points are placed appropriately, agentic AI can become a valuable support tool. Conversely, if it is deployed without adequate preparation, the speed of automation may only cause errors to spread more quickly.
