


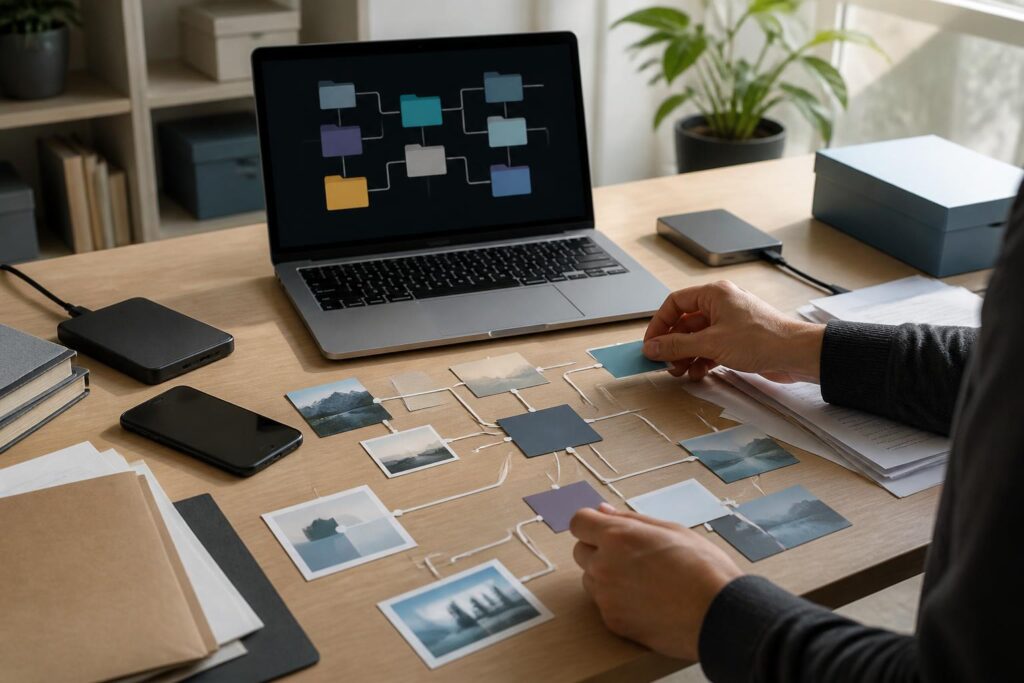
Privacy is often discussed as a technical or legal issue, but most risks actually begin with very ordinary habits. A user may sign up for multiple services using the same email address, store photos of documents in numerous applications, allow dozens of programs to access their location, or use one phone number for a long time without remembering which organizations they provided it to. When data is scattered in this way, protecting information becomes difficult not because users do not care, but because they lack an overall picture.
A practical approach is to create a “personal or family privacy map.” This is not a special piece of software, nor does it require advanced technical knowledge. It is a structured record of the types of data one possesses, where the data is stored, who may access it, the purposes for which it is used, and how it is handled when no longer needed. This map helps shift information protection from a passive reaction to a proactive process that can be reviewed and improved over time.
Start by identifying which data is truly important
Not all information has the same level of sensitivity. A useful map should classify data according to the impact if it is exposed, lost, or misused. Basic contact information such as a display name, an email address used to subscribe to newsletters, and an alternate phone number may be placed in the category requiring control. Meanwhile, identity documents, financial information, health records, biometric data, information about children, and data that allows access to accounts should be considered more sensitive.
The classification does not need to be overly complex. It can be divided into three levels: public information, personal information requiring restrictions, and sensitive information requiring strict protection. A landscape photo posted publicly usually does not carry the same risks as a photo of an identity document. A delivery address stored with an online retailer is also different from the login information for a payment account. Placing data in the right category helps users allocate their efforts appropriately instead of trying to protect everything in the same way.
When making a list, do not think only of the data currently stored on a phone or computer. Also include data in email, messaging applications, cloud storage services, shopping accounts, learning platforms, records at healthcare facilities, bank accounts, household devices, and paper forms. Small pieces of information, when combined, can create a fairly complete picture of a person’s habits, residence, schedule, and relationships.
Map data according to where it is stored and how it travels
After identifying the data categories, the next step is to record where they are stored. A simple table may include the following columns: type of data, storage location, purpose for providing it, people or organizations that may have access, date of the most recent review, and action needed. There is no need to record details that are uncertain. The important thing is to create an initial map and then add to it as more information becomes available.
For example, an email address may appear in a social media account, an online store, a ticket-booking service, and several newsletters. A phone number may be used to log in, recover a password, or receive transaction notifications. Personal photos may simultaneously exist in the phone’s library, a cloud backup, and conversations. If only one device is checked, users will overlook other copies that may still exist.
The path data takes is no less important than where it is stored. When a form is filled out, the information may be transferred to a customer service department, a technical service provider, or a payment-processing partner. Users do not always need to track every system behind the scenes, but they should know what data is collected for and whether providing that information is truly necessary. If the purpose is unclear, that is a sign to read the explanatory information carefully, ask the provider for clarification, or consider not proceeding.
Check access permissions instead of checking only passwords
Strong passwords remain important, but privacy also involves the accounts and applications that are allowed to access data. An application may not know an email password but may still be granted permission to read contacts, view location, or connect to another account. Therefore, reviewing access permissions should be done separately rather than combined with changing passwords.
Review the list of applications installed on the phone, each application’s permissions, and the third-party accounts that are linked. Does a photo-editing application need to know the precise location? Does a game need access to contacts? Does a service that has not been used for a long time still have permission to connect to email? These questions do not assume that every request is dangerous, but they help users recognize permissions that were granted out of habit.
Revoke permissions that are no longer needed, remove old connections, and delete unused applications. If a service requests permissions beyond the function the user expects, consider finding an alternative or granting only the minimum level of access. On many devices, access can be set to allow it only once, only while the application is in use, or not at all. The appropriate choice will reduce the amount of data shared continuously.
Reduce redundant data and unnecessary copies
One of the most effective ways to protect data is not to retain too much information that no longer has value. Old accounts, snapshots of forms, email attachments, and duplicate photos often remain longer than their actual need. They take up space, make searching more difficult, and expand the scope of damage if an account or device is compromised.
You can begin with a small cleanup, such as reviewing the downloads folder, screenshots, and emails containing sensitive data. Files that do not need to be kept should also be deleted from the trash if the device or service has a temporary-storage mechanism. For documents that need to be retained, use clear file names, move them to a suitably protected location, and avoid creating multiple uncontrolled copies.
Deleting data does not mean immediately deleting everything. Some documents may be needed for warranties, taxes, education, healthcare, or disputes. Before deleting anything, determine how long it needs to be kept and where the original will be stored. For important records, a well-protected backup may be more useful than keeping scattered copies across multiple devices. The principle should be to retain enough for legitimate and practical purposes, not indefinitely simply because it has never been reviewed.
Establish sharing principles within the family
Personal privacy is often affected by the habits of people living in the same household. One member may share photos of another person, store photos of documents in a group chat, or allow a child to use a shared account without realizing what information is being made public. Therefore, families should have simple, easy-to-remember principles rather than issuing reminders only after an incident occurs.
Before posting a photo that includes someone else, ask for their consent if the content could reveal their residence, school, schedule, or private information. Photos of children require more careful consideration because children may not yet be able to understand the consequences of long-term sharing. Family members should also agree not to send photos of documents, authentication codes, or financial information to large group chats unless it is truly necessary.
For shared accounts, clearly distinguish between usage rights and administrative rights. Do not share one password across all services simply for convenience. If several people need access to a resource, use separate permission features if the service supports them. When a member no longer uses an account, their access should also be reviewed, especially for accounts related to family matters, work, or finances.
Turn the map into a periodic review process
A privacy map will quickly become outdated if it is created once and then forgotten. However, it is not necessary to check it every day. A periodic review schedule, quarterly or semiannually, may be suitable for many people. Each time, focus on one group: online accounts, phone applications, stored data, household devices, or publicly shared information.
After each review, record a few specific actions that can be completed, such as deleting an old account, revoking location access, changing the account-recovery method, or moving sensitive documents out of a shared folder. An overly long list can easily cause users to procrastinate. The goal is not to achieve a perfect state, but to continuously reduce the clearest weaknesses.
The map should also be updated when major changes occur, such as changing a phone number, moving to a new residence, beginning to use a new financial service, changing jobs, or purchasing an Internet-connected device. These moments often involve providing additional data and creating new accounts. Checking immediately after a change will help prevent old information from continuing to exist in multiple places that the user no longer remembers.
Privacy is a matter of choices and degree
There is no way to completely eliminate data sharing in modern life. Many services need certain information to provide products, process transactions, or support users. The practical goal is not to refuse every request, but to understand what one is trading away, share only what is necessary, and be able to adjust when needs change.
A good privacy map does not need an elaborate format. It can be a protected spreadsheet, a document stored securely, or a separate list that is updated regularly. Its value lies in helping users see the dispersed points of their data, recognize excessive access permissions, and make more deliberate decisions. When people know where their data is, who can access it, and why it is being retained, they will have a stronger foundation for protecting their information against risks that are difficult to see.
