


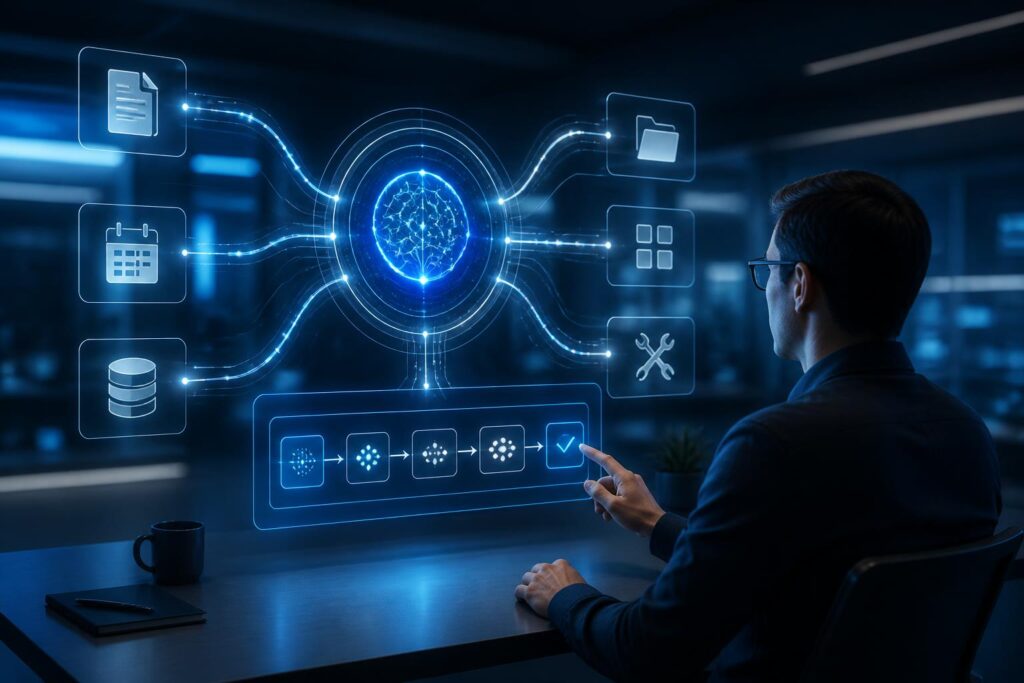
In the early stages of the generative AI wave, most users became accustomed to a fairly simple way of interacting: ask a question, receive an answer, then check it themselves and handle the remaining work. This model remains useful, but another approach known as agentic AI is emerging. Rather than merely generating a response in a single turn of conversation, agentic AI is designed to pursue a goal, break that goal down into multiple steps, use appropriate tools, and adjust its actions based on the results it receives.
This concept is easy to confuse with an ordinary chatbot. The difference does not lie in whether the system can write a long or short answer, but in how it participates in a workflow. A chatbot typically waits for the user to ask each question and responds only within the scope of the direct request. An AI agent can be assigned a broader task and then determine the necessary intermediate steps on its own. Even so, “autonomy” in this case does not mean that the machine has thoughts, will, or responsibility like a human. It is a way of describing a software system capable of choosing actions within predefined limits.
How Does Agentic AI Operate?
An agentic AI system usually begins with a goal provided by a user or organization. That goal might be to compile information from a set of documents, classify customer requests, prepare a draft report, or monitor an internal process. To reach the desired result, the system needs to interpret the request, make a plan, select tools, carry out each step, and evaluate the output.
The tools involved may include the ability to search a data repository, read files, perform calculations, call a software service, or update an authorized system. A language model does not automatically have access to all data or the ability to perform every action. Those permissions must be connected and restricted through software. In practice, therefore, an AI agent is a combination of an AI model, memory or context, external tools, and control rules.
The process can be illustrated simply: the system receives a goal, proposes a plan, completes one step, observes the result, and then decides what to do next. If the result does not meet requirements, it may try another approach or ask a human to provide additional information. This loop makes agentic AI more suitable for multistep tasks, but it also increases the risk of errors if the initial goal is vague or the permissions granted are too broad.
The Difference Between Answering and Performing Work
With a question-and-answer tool, the user is usually responsible for turning the answers into concrete actions. For example, AI may suggest a plan, while the user checks the data, chooses an option, and enters the information into the relevant systems. With agentic AI, part of that chain of actions is transferred to the software. The system does not merely say “what should be done”; it may prepare documents, organize information, or carry out permitted operations.
This difference can help reduce repetitive work. Employees do not necessarily have to transfer data manually across multiple steps if the systems have been connected properly. Users can also focus more on defining goals, reviewing exceptions, and making the final decision. However, automating a process does not automatically make that process correct. If the input request is unclear, the data is incomplete, or the processing rules are unsuitable, an AI agent may carry out the wrong action faster than a human.
Situations in Which Agentic AI May Be Useful
In office work, an AI agent can help collect information from specified documents, summarize key points, and create drafts based on a template. In customer service, the system can classify requests, find relevant content in a knowledge base, and suggest a response before an employee sends it to the customer. In project management, it can track tasks, remind people about missing information, and compile status updates from multiple sources.
In education, an AI agent can help learners build a study plan, divide a broad subject into smaller sections, and adjust practice exercises based on their previous answers. The value here is not to have the machine completely replace teachers or instructors, but to create a support tool capable of following progress more closely than a single answer can.
On a personal level, an agent can help organize information, prepare task lists, or remind users to check steps they may have missed. Although these applications may seem simple, they still need to be designed carefully if they involve work schedules, private data, or actions with real-world consequences.
Risks Increase When AI Is Given More Permissions
The first risk is that the goal may be misunderstood. A request such as “process all outstanding requests” may lack criteria concerning priority, data scope, and stopping conditions. If the system makes too many assumptions, it may choose an inappropriate action even while trying to complete the task.
The second risk concerns data. An AI agent may need to read internal documents, customer information, or content containing sensitive data. Connecting multiple sources increases the need for clear access controls. Not every agent needs permission to view entire records, and it certainly should not automatically have permission to edit information or send it externally.
The third risk is that an error can spread across multiple steps. An inaccurate answer in a conversation can often be identified and corrected immediately. By contrast, if an error occurs at the beginning of an automated process, later steps may rely on incorrect information and produce results that are harder to detect. The level of danger depends on the field, the type of data, and the system’s authority to take action.
In addition, users may develop excessive trust when an agent presents its results coherently. Clear wording is not evidence that the data has been fully checked. Even a good system can make incorrect assumptions, overlook exceptions, or misjudge the level of certainty associated with information.
What Role Should Humans Retain?
In processes with significant effects on finances, rights, safety, or reputation, humans need to be placed at appropriate control points. This does not necessarily mean approving every minor operation. The system can be designed to handle low-risk steps on its own, but it should stop when it encounters an action that cannot easily be reversed, sensitive data, or a situation outside the usual rules.
Users also need to assign tasks in a specific way. A good request should state the goal, data scope, completion criteria, limits on authority, and situations requiring confirmation. The less ambiguity there is, the more basis the system has for acting consistently. For important tasks, users should ask the agent to present its plan, the data sources it used, and any uncertainties before carrying out the final step.
For organizations, deploying agentic AI should not be viewed merely as purchasing another tool. They need to determine who owns the process, who is responsible when errors occur, what data may be used, and how the history of actions will be recorded. These are governance questions and cannot be solved simply by choosing a more powerful model.
Deploy Step by Step Rather Than Granting Immediate Authority
A cautious approach is to begin with tasks that have a clearly defined scope, outputs that are easy to check, and low consequences if an error occurs. At the initial stage, AI may only be allowed to read data and suggest actions, without permission to send, delete, or alter information on its own. After the process has been evaluated, its permissions can be expanded within specific limits.
Checking also needs to continue after the system has been put into use. Data changes, connected tools may encounter errors, and user requests are not always the same. Therefore, it is necessary to monitor cases in which the system stops, instances when humans have to correct the results, and types of tasks that commonly cause confusion. These observations help improve instructions, access permissions, and approval processes.
Agentic AI has the potential to change the way humans delegate tasks to machines. Instead of breaking down every operation and waiting for a response at each turn, users can describe a goal at a higher level while the system handles part of the intermediate work. But the value of this approach does not lie in granting as many permissions as possible. Its real value comes from balancing automation capabilities, the ability to check results, and human responsibility.
In the future, the important question may not be only what AI can do, but also what it is allowed to do, under what conditions, and who will intervene when the result is wrong. Understanding agentic AI in this way helps users avoid both extremes: expecting machines to solve everything on their own, or denying the practical benefits of controlled automation.
