


In most online services today, a person’s identity is usually distributed across many places. One application stores an email address, another platform keeps payment information, while financial services may additionally require documents, biometric data, or transaction history. Users repeatedly provide similar information to many organizations, yet have little ability to know where the data is stored, with whom it is shared, or how long it will exist.
Blockchain does not automatically solve this entire problem. However, the characteristics of a distributed ledger, the ability to verify data, and digital signature mechanisms have opened up a different approach: decentralized digital identity. Instead of allowing a single platform to stand in the middle and control users’ records, this model aims to let individuals retain control over their identity information, while organizations only confirm the attributes necessary for each transaction.
This is a topic with considerable potential, but it is also easy to interpret too optimistically. Blockchain can support trust between parties, but it cannot turn false information into true information, nor can it eliminate risks arising from devices, access keys, or legal regulations. The practical value of decentralized identity therefore lies in how the entire system is designed, not merely in putting some data on a blockchain.
How Is Decentralized Identity Different from an Ordinary Online Account?
In the traditional account model, a service provider usually creates and manages a user’s identity. Users register an account, set a password, or use a login method provided by the platform. The platform may decide what data is collected, how the data is verified, and how access is maintained. If the system is disrupted, locked, or attacked, users may lose access to their accounts and related services.
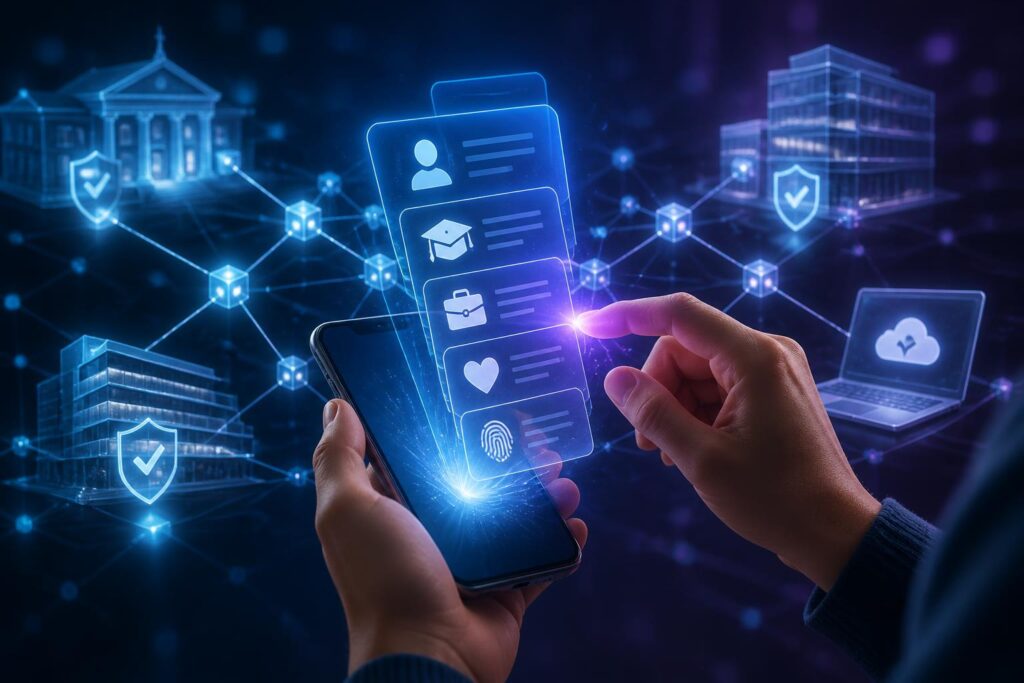
Decentralized digital identity, often described through the concept of user-controlled identity, changes this role. An individual can own a digital identifier linked to a cryptographic key pair. The organization issuing the credentials, such as an educational certificate, professional license, or age verification, signs that data. The user stores the credentials in a digital wallet and presents them to the party that needs to verify them.
The important point is that the verifier does not necessarily have to receive the entire original profile. If a service only needs to know whether a user meets the applicable age requirement, the system can aim to prove that attribute instead of requesting the full date of birth. If an employer needs to know whether an applicant has completed a training program, it can verify a certificate issued by the training provider without having to call or email each institution manually.
What Role Does Blockchain Play in the System?
Blockchain is generally not the place where all identity data is stored. Uploading personal documents, medical records, or biometric data to a public ledger would create major risks to privacy and the ability to delete data. A more appropriate role for blockchain is to provide a shared verification layer, where parties can confirm public keys, the status of a credential, or the identity of the issuing organization.
For example, when a school issues an electronic certificate, the detailed information can be sent directly to the learner’s wallet. The blockchain network only needs to record the minimum data necessary for parties to later know which key belongs to the issuing institution or whether a certificate is still valid. When the learner presents the certificate, the receiving party can check the digital signature and compare it with publicly available information without relying on a single database.
This separation helps reduce the amount of sensitive data that appears on the network. Nevertheless, it does not eliminate risk entirely. Transaction trails, wallet addresses, or verification times may still reveal links between activities if the system is designed carelessly. Therefore, privacy must be taken into account from the outset, rather than being treated as an additional feature after the product is already operating.
Three Roles That Need to Be Distinguished
In a decentralized identity system, three main groups can be distinguished. The subject is the person or organization that owns the identity and uses the credentials. The issuer is the organization that creates and signs the certificate, such as an educational institution, business, or authorized agency. The verifier is the entity that receives the information and assesses whether the certificate meets the requirements of a service.
This division does not mean that all roles are completely independent. A company may both issue certificates to its employees and verify information about its partners. What matters is that each party’s responsibilities are clearly defined. If data is incorrect, if a key is exposed, or if a certificate needs to be revoked, the system must indicate who has the authority to handle the matter and where users can file complaints.
Practical Benefits for Users and Organizations
The most obvious benefit is reducing the repeated provision of the same type of information. Users can store verified credentials and use them across multiple compatible services. This can shorten the processes of opening an account, enrolling in a course, proving qualifications, or accessing a service that requires eligibility checks.
The ability to share selectively is also notable. In the traditional model, users sometimes have to send a copy of an entire document just to prove a small detail. Decentralized identity can support verification methods that disclose less data, provided that the protocols and applications are built correctly. Users still have to decide what information to share, with whom, and for how long.
For organizations, digital credentials can reduce the cost of manual verification and limit the handling of inconsistent paperwork. A business can verify the origin of a professional certificate or authorization status without maintaining multiple separate connections with issuing authorities. In an environment with many partners, a shared verification layer can make coordination processes clearer.
This model may also support people who often have difficulty proving their identity. People moving between countries, freelancers, or those who no longer retain complete paper records may use digital credentials that were issued previously. However, this capability is meaningful only if organizations adopt compatible standards and users have a secure recovery option when they lose a device or access key.
Obstacles That Blockchain Alone Cannot Solve
The first challenge is the private-key problem. In a traditional system, users can request a password reset through the provider. With an identity tied to a cryptographic key, losing the key may prevent users from proving ownership. If the key is stolen, a malicious party may sign or present information on behalf of the owner. Therefore, social recovery mechanisms, backup devices, or digital guardians need to be carefully studied, but each mechanism creates new points of dependence.
The second challenge is revocation. A degree, license, or access right may need to be canceled after it has been issued. Blockchain can record revocation status, but the receiving application must actually check that status. If a service only verifies the signature without checking whether the credential is still valid, an old certificate may still be misused.
The third challenge concerns the quality of input data. Blockchain can help prove that a record came from a particular key and has not been altered, but it cannot by itself confirm that the content of the record is correct. If an organization mistakenly issues a certificate or deliberately enters false information into the system, immutability only causes the incorrect data to be recorded for longer. Auditing mechanisms, issuer accountability, and dispute-resolution procedures therefore remain essential.
Interoperability is also a major barrier. A person may possess multiple wallets, identifiers, and types of credentials but be unable to use them if platforms do not understand the same standard. The user experience will become complicated if each service requires a separate application, format, or authentication process. Decentralized identity can only develop widely when the underlying technical layer is sufficiently unified and the front-end interface is sufficiently simple.
Privacy Must Be Designed as a Principle
Digital identity should not be understood as a single profile containing all information about a person. A safer approach is to divide attributes into parts, share only what is necessary, and limit the ability to link different transactions to the same identifier. A person may use different identifiers for different contexts, as long as there is still a mechanism to prove validity when necessary.
Giving users control does not mean assigning all responsibility to them. Wallet-management applications must clearly explain what data is being shared, what a signature means, and how access can be revoked. Technical terms that are difficult to understand or confusing interfaces may cause users to sign requests they do not fully understand.
For organizations, the principle of data minimization should be placed on an equal footing with verification requirements. They should not request all information merely because the system is capable of receiving it. A good process must answer the questions: what data is truly necessary, who can view it, how long will it be stored, and how can users request the modification or deletion of off-chain data?
Conditions for This Model to Move Toward Mass Adoption
First, decentralized identity needs to provide an experience that is simpler, or at least no more inconvenient, than the current method. Ordinary users should not have to deeply understand private keys, network fees, or consensus mechanisms in order to prove a basic attribute. The technology may be complex behind the scenes, but the user process must be clear and include support options when problems occur.
Next, issuing and verifying organizations must have specific responsibilities. Standards for issuing credentials, procedures for handling errors, revocation processes, and verification methods for when the system is offline must be defined. A digital credential creates value only when the receiving party trusts the issuer’s reputation and can independently check the credential’s status.
Finally, there must be a legal framework and coordination among the parties. Identity is directly connected to privacy, contracts, financial services, education, and many other civil activities. If the law has not clearly defined the value of digital credentials or responsibility when a key is exposed, businesses will find it difficult to incorporate the system into critical processes. Blockchain can provide verification infrastructure, but validity in everyday life still depends on institutions and social trust.
Decentralized digital identity therefore should not be promoted as a promise to eliminate all intermediaries. A more realistic goal is to redistribute control over data, reduce unnecessary sharing, and create a verifiable method of authentication across multiple organizations. The success of this model will not be measured by the number of wallets created, but by whether users can use their identities safely, understandably, and with the ability to recover them when problems occur.
